Electronic signatures have become routine for engagement letters, settlement documents, and countless forms that once had to be printed, signed, and scanned. Clients like the convenience, and attorneys like not chasing paper. The signature itself is rarely the concern.
The concern is everything around it. An e-signature platform holds the documents being signed, the identities of the people signing them, and a record of who did what. For a law firm, that makes it another place where confidential client information lives.
Are Electronic Signatures Valid?
Generally, yes. Federal law and Texas law both recognize electronic signatures and records in most transactions, and the Texas Uniform Electronic Transactions Act sits in Chapter 322 of the Business and Commerce Code. Certain categories of documents, such as wills, are typically treated differently, and some situations carry their own requirements, so the firm's attorneys should confirm what applies to a particular document.
That validity depends on the process being sound. A signature is only as trustworthy as the evidence of who signed, when, and whether the document changed afterward. This is where a platform's security features start to matter.
Security Features Worth Looking For
When comparing tools, these are the capabilities that bear most directly on protecting client documents and the integrity of the signing:
- Signer identity checks: options beyond simply clicking an emailed link, such as access codes or additional verification for higher-stakes documents
- Multi-factor authentication for firm users, so that a stolen password does not open the account and every document in it
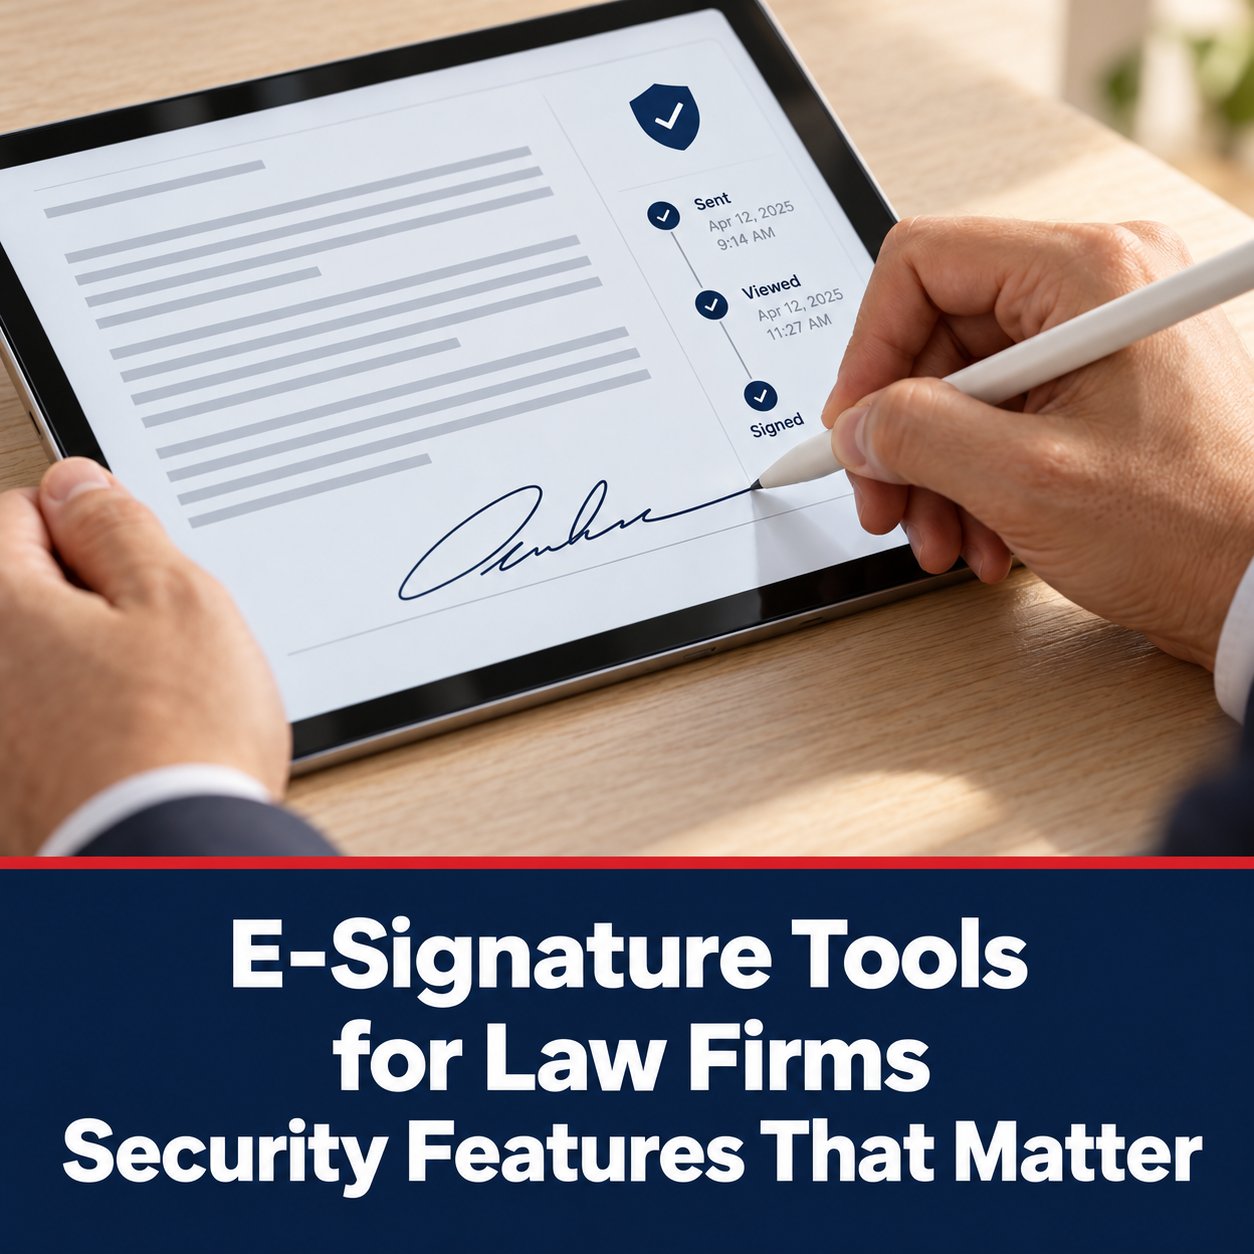
- A complete audit trail: a record of when each document was sent, viewed, and signed, preserved with the finished document
- Tamper evidence: sealing the document once it is signed so that later changes are detectable
- Encryption for documents while they are being sent and while they are stored
- Role-based access, so staff can send and track only the documents they should
- Control over retention: the ability to download completed documents and their audit records, and to have them deleted from the platform when the firm chooses
Questions About the Vendor
As with any cloud service, the firm is trusting a vendor with client material. It is reasonable to ask where documents are stored, who at the vendor can access them, whether they are used for any purpose beyond providing the service, how long they are retained, and what independent security documentation the vendor can provide. The firm should also consider how the tool fits with the systems it already uses, such as practice management and document storage, so that signed documents end up in the right matter file rather than scattered across inboxes.
The Risk That Comes With Familiarity
Because signature requests are now an ordinary part of business, they are also a popular disguise for phishing. A fake notice that appears to come from a signature service, asking the recipient to sign in to view a document, is a common way to capture credentials. Staff should know what legitimate requests from the firm look like and how to confirm a suspicious one, and clients benefit from being told what to expect when the firm sends a document for signature.
Making a Choice
Most firms will do well to pick one approved platform rather than allowing several, set it up with multi-factor authentication and sensible access rules, and decide in advance where completed documents will be filed. The goal is a signing process that clients find easy and that the firm can later demonstrate was handled securely.
Frequently Asked Questions
Are electronic signatures legally valid in Texas?
In most transactions, yes. Federal law and the Texas Uniform Electronic Transactions Act, found in Chapter 322 of the Business and Commerce Code, recognize electronic signatures and records. Some documents, such as wills, are generally treated differently, so attorneys should confirm the rules for a specific document.
What is an audit trail, and why does it matter?
An audit trail is the record of when a document was sent, viewed, and signed, and by whom. It is the evidence that supports a signature if it is later questioned, so it should be preserved with the completed document.
Do e-signature tools need multi-factor authentication?
Firm users should have it. Without it, a single stolen password could expose the documents in the account. Many platforms also offer extra verification for signers when a document warrants it.
Where should signed documents be stored?
In the matter file within the firm's approved document storage or practice management system, not left only in the e-signature platform or in email. The firm should keep the finished document together with its audit record.
How can clients tell whether a signature request is genuine?
The firm can tell clients in advance how requests will arrive and who they will come from, and encourage them to call if anything looks unexpected. Staff should apply the same caution to requests they receive.
Next Step
If your firm is choosing or reviewing an e-signature tool and wants a plain look at how it protects client documents, we offer a 15-minute call to see if we're a fit. No pitch, no obligation.
Managing partners and office administrators can reach us at 325-643-8184 or through the contact form at apollocomputers.com.